Skip to content

Available for engagements - Brașov, Romania

Available for solo engagements or team-led assessments with trusted security professionals.

Petre Radu
Cătălin
- Offensive Security Professional

Penetration Tester @ NTT DATA

Offensive Security · Bug Bounty · Cloud & AI Security

I'm Petre Radu Cătălin, an offensive security professional focused on penetration testing, security research, and practical risk assessment. I work on real-world web application and infrastructure testing, then turn findings into clear remediation paths.

  • Penetration Testing
  • Bug Bounty Research
  • Cyber Security Studies
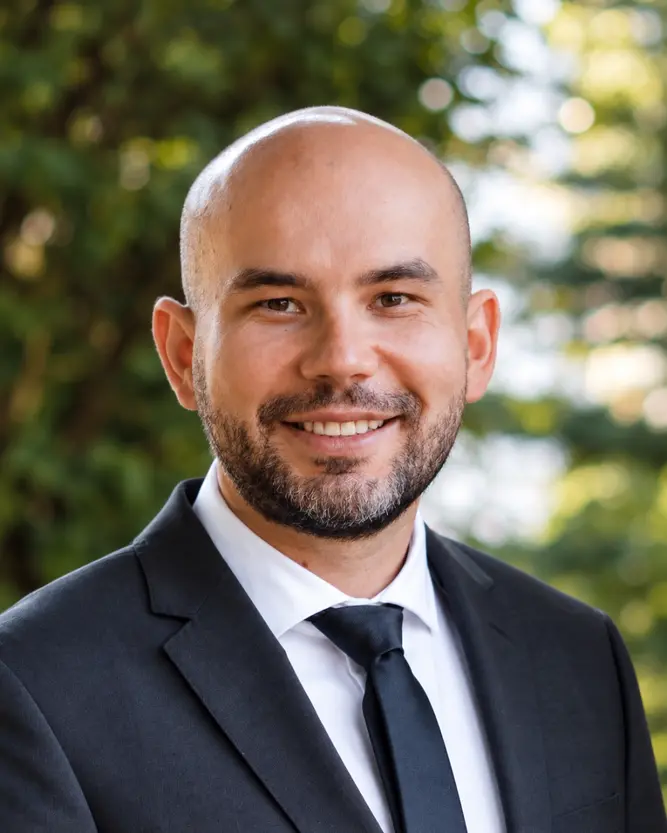
Petre Radu Cătălin - Penetration Tester based in Brașov, Romania
● ONLINEsituated: BRASOV, RO

// whoami

About Petre Radu Cătălin

Offensive security professional and penetration tester based in Brașov, Romania. Known as Petre Radu to clients, peers, and the security community.

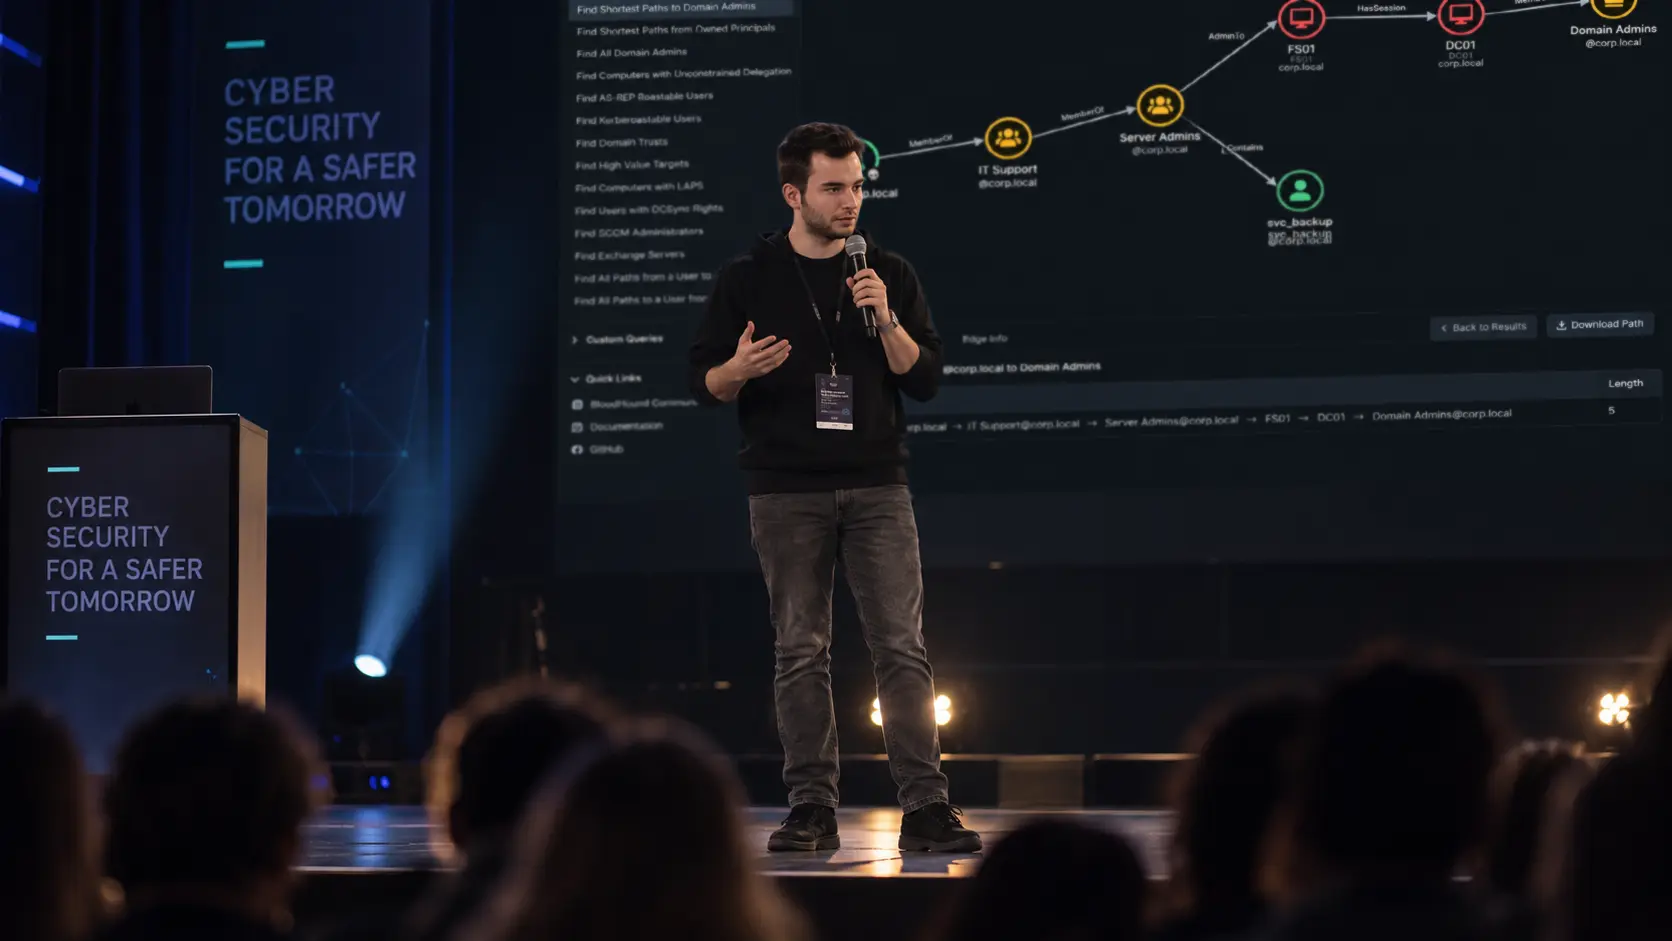
Petre Radu Cătălin presenting on stage at a cybersecurity conference

Who I am

I'm Petre Radu Cătălin, an offensive security professional focused on penetration testing, bug bounty research, and practical security evaluation. I work as a Penetration Tester at NTT DATA and am based in Brașov, Romania.

My philosophy

I approach security with a practical mindset: focus on the issues that matter, validate how they can be exploited, and turn them into clear remediation steps that teams can act on. The goal is not just to find flaws, but to explain the real risk and support the fix.

The journey

My academic path includes a Master's degree in Cyber Security at Universitatea Transilvania din Brașov (2024-2026), alongside a Bachelor's in Renewable Energy Systems completed there between 2020 and 2024. This mix of study and hands-on practice has shaped my understanding of systems, networks, and security testing.

Beyond testing

I also engage in vulnerability research through bug bounty programs on Intigriti and HackerOne, which keeps my work grounded in real-world exposure and responsible disclosure. I continue expanding my skills through security training, labs, and CTF-style exercises.

Learning mindset

I value continuous learning and hands-on practice. Security is always evolving, so I stay engaged with training, tooling, and applied research across web, infrastructure, and defensive concepts.

How I work with others

For larger scopes, I collaborate with a small network of vetted professionals across offensive security, cloud, compliance, and incident response. I remain the main point of contact, while bringing in specialists when the assessment requires deeper coverage.

3
Current roles
2
Degrees
2+
Years of work
CTF
Practice

// partners

Trusted Collaborators

For larger scopes, I work with a small network of vetted professionals to bring in deeper coverage when an engagement needs additional specialist support.

Marius Galmati - IT & Cybersecurity Consultant

Marius Galmati

BITUP Technology

Partner

IT & Cybersecurity Consultant

Specialty: IT governance, cyber risk management, ISO 27001 / NIS2 readiness, security controls

Role: Ten+ years across systems, IT infrastructure, and ISO 27001 audit readiness; brings IT governance, cyber risk, and NIS2 compliance expertise to governance-heavy engagements.

Contact: Available on request
// capabilities

Expertise

Four interlocking disciplines. My offensive work is grounded in an understanding of defense - every assessment I run, from web penetration testing to cloud security review, is built to produce actionable defense.

Offensive Security

Hands-on exploitation across the full attack surface - from web apps to the domain.

  • Web & API penetration testing (OWASP Top 10)
  • Active Directory exploitation & privilege escalation
  • Network security audits
  • Red Team emulation aligned to MITRE ATT&CK
  • Automated recon & exploit development (Python, Bash)

Cloud & AI Security

Breaking and hardening modern, ephemeral attack surfaces before attackers do.

  • Multi-cloud assessments (AWS, Azure, GCP)
  • IAM & identity misconfiguration exploitation
  • AI/ML security evaluations
  • Cloud incident response

Compliance & Governance

Turning regulatory requirements into measurable, defensible security posture.

  • GDPR assessments & data protection reviews
  • NIS2 implementation support
  • Security policy review
  • Technical risk assessment

Defensive Foundation

Knowing the defender's playbook sharpens every offensive engagement.

  • SIEM / SOAR engineering (Splunk)
  • Threat hunting & detection engineering
  • Secure code review
  • Purple-team collaboration

// history

Experience

Penetration testing, bug bounty research, and hands-on security work shaped by real-world findings and practical remediation guidance.

Engagement model: for broader scopes, I coordinate complementary work with trusted specialists in cloud, compliance, and incident response. I remain the primary point of contact and lead the assessment flow from scoping through reporting and remediation validation.

  1. I

    Intigriti

    Freelance

    Bug Bounty Hunter

    May 2026 - PresentRemote

    • Conduct vulnerability research and bug bounty testing on public programs.
    • Focus on web application and API security, business logic flaws, and responsible disclosure.
    • Use Burp Suite and related tooling to validate findings and communicate impact clearly.
  2. ND

    NTT DATA, Inc.

    Full-time

    Penetration Tester

    Nov 2025 - PresentRomania · Remote

    • Perform penetration tests on enterprise web applications and infrastructure.
    • Assess production environments to identify security weaknesses and validate risk.
    • Provide actionable findings and remediation guidance to engineering and security teams.
  3. H

    HackerOne

    Freelance

    Vulnerability Researcher

    May 2025 - Sep 2025Remote

    • Performed independent vulnerability research through bug bounty programs.
    • Identified and reported issues such as XSS, IDOR, CSRF, and access control flaws.
    • Worked through responsible disclosure and collaborated with program owners on remediation.
  4. Universitatea Transilvania din Brașov

    Master's degree, Cyber Security

    2024 - 2026

    • Studied advanced topics in cyber defense, ethical hacking, cryptography, and secure software development.
    • Worked with tools such as Wireshark, Burp Suite, Splunk, Wazuh, and Suricata.
    • Participated in cybersecurity labs, practical simulations, and CTF-style exercises.

// featured_work

Projects

Selected projects from research, development, and real engagements - static malware analysis, forensic tooling, and the automation that powers my assessments.

MalwarePeek - PE File Analyzer for Static Malware Analysis project by Petre Radu Cătălin

MalwarePeek

PE File Analyzer for Static Malware Analysis

MalwarePeek is a Python-based portable executable analyzer built for malware analysts and reverse engineers. It parses PE headers, fingerprints packers, and scans samples against YARA rules - then generates clean HTML reports for triage.

Python
Malware Analysis
Reverse Engineering
Signature Stealer - Educational PoC - Authenticode Signature Extraction project by Petre Radu Cătălin

Signature Stealer

Educational PoC - Authenticode Signature Extraction

A focused educational proof-of-concept that inspects authenticated code-signing metadata inside signed PE files. It demonstrates how signature blocks remain queryable and how tooling can surface embedded certificate chains for forensic review.

Python
Digital Forensics
Reverse Engineering
Custom Pentest Automation Toolkit - Recon & Vulnerability-Scanning Automation project by Petre Radu CătălinPrivate

Custom Pentest Automation Toolkit

Recon & Vulnerability-Scanning Automation

An internal toolkit of Python and Bash scripts that automate reconnaissance, endpoint enumeration and vulnerability scanning. Used to deliver faster, repeatable assessments and cut end-to-end testing time by roughly 30% at NTT DATA.

Python
Bash
Automation
Offensive Security
Private repoCase study

// credentials

Certifications & Achievements

Focused cybersecurity training, hands-on practice, and participation in security exercises that sharpen real-world testing skills.

Selected Security Training

Curated highlights below from coursework, labs, and CTF-style practice.

eLearnSecurity Certified Penetration Tester (eCPPT)

INE / eLearnSecurity

OpenAI Cyber Practitioner

OpenAI · PartnerU

Microsoft AI Skills Fest 2026

Microsoft

AZ-700: Azure Networking Solutions

Microsoft Certified

Teaching the AI Fluency Framework

Anthropic

Puppet Environment Lab

Skillsoft

Google.org Cybersecurity Seminars

Google.org

CTF Achievements

Offensive security is a competitive sport. These results are how I train between engagements.

  • HackTheBox Season 9

    Participation

  • TryHackMe Industrial Intrusion CTF

    Participation

  • TryHackMe Honeynet Collapse CTF

    Participation

// arsenal

Tools Arsenal

The tools I reach for daily - offensive platforms, cloud CLIs, and the defensive stack I know well enough to test around.

tools.sh

Cobalt Strike

Sliver

Nighthawk

BloodHound CE

SharpHound

Rubeus

KrbRelayUp

NetExec

Impacket

Responder

Evil-WinRM

Ligolo-ng

Burp Suite Pro

Nuclei

ffuf

Pacu

AzureHound

GCPwn

Prowler

Garak

$ echo "recon --enumerate --exploit --report" | sudo tee /dev/arsenal

// write_ups

Insights from Petre Radu Cătălin

Technical write-ups on offensive security, cloud threats, and AI security - the lessons from real engagements, published to help the community.

9 min read

From Web App to Domain Admin: A Red Team Playbook

A practical, phase-by-phase breakdown of how a single web application flaw can be chained into full Active Directory compromise - and the detection gaps that let it happen.

Penetration Testing
Red Team
Active Directory
Read More

// connect

Work with Petre Radu Cătălin

Available for remote and on-site engagements. Based in Brașov, Romania.

Engagement type: solo / team-led assessment. I can lead the engagement directly or coordinate with trusted specialists for broader coverage.

Requests open the email client - no data is stored on this site.